Video
AI WEAPONIZEDNovember 12, 2026
Operation Snowball: Jailbroken DeepSeek AI Agent Runs 14-Day Autonomous Intrusion Into European Telecom
Read

Actionable threat intelligence, delivered daily.
Free. No spam. Trusted by 50,000+ practitioners. Unsubscribe anytime.
New subscribers also get: The Mythos Brief (AI zero-day research, free)
Reach 50,000+ security professionals
Sponsor a newsletter slot and put your brand in front of CISOs, engineers, and IT decision-makers.
wfx-loot hijacked 4,837 GitHub accounts to steal CI/CD cloud credentials that persist past token rotation across 61,764 repos. Audit and rotate now.
1705 briefings published · full archive of every threat intelligence report.
Browse All IntelligenceWe monitor hundreds of sources across every threat category. Each morning we identify the single most critical, most actionable threat and tell you exactly what to do about it.
When a new exploitable vulnerability emerges before a patch exists, we cover it the morning your window to act opens.
Active ransomware groups, fresh victims, TTPs in play, and the sectors in the crosshairs right now.
APT activity, espionage campaigns, and state-sponsored attacks with enough detail for defenders to act.
Misconfigurations, credential leaks, and open attack surface gaps that leave your organization visible to attackers.
Credential-harvesting operations targeting your sector, including AI-enhanced and business email compromise attacks.
Compromised packages, vendor incidents, and third-party risk events with real downstream blast radius.
Anthropic's Project Glasswing red team confirmed autonomous zero-day discovery across every major OS and browser, with some bugs buried for over two decades. Updated October 2026: Mythos 5.1 is now in limited release via the Cyber Verification Program; Bank of America spent $200M+ in Q3 patching Mythos-found flaws using 4,000 workers. Most vulnerabilities across 200+ partner organizations are still unpatched.
21/41
V8 ACEs in ExploitBench; no other model scored above zero
10.5×
More exploits than Opus 4.6 (ExploitGym benchmark)
$35M
Smart contract value identified in SCONE-Bench
What's inside the brief
Free Practitioner Brief
Claude Mythos Preview: What Security Teams Need to Know Now
Sourced from Anthropic's Project Glasswing red team assessment (April 2026), Exploit Evals benchmark report (May 2026), and October 2026 developments including Mythos 5.1 release and Bank of America Q3 earnings disclosure. Written for security engineers and CISOs. No vendor pitches, no padding.
You'll also receive the Decryption Digest: daily threat intelligence for practitioners. Unsubscribe any time.
Already subscribed? Go directly to the brief →
Trusted by 50,000+ SOC analysts, CISOs, and security engineers
Free resources
25 actively exploited vulnerabilities with CVSS scores, exploit status, and patch availability. Print it, pin it, share it with your SOC team.
Step-by-step 24-hour IR checklist covering detection, containment, eradication, and recovery. Built for SOC teams, IR leads, and CISOs.
The threat landscape doesn't pause overnight. By the time you open your laptop, actors have moved, disclosures have dropped, and your patching window is narrowing. Most security teams are playing catch-up before 9am.
Your SIEM fires thousands of alerts before breakfast. Critical CVEs get buried. By the time triage completes, the patching window has already closed. Threat actors have already moved.
Threat actors exploit within hours of disclosure. Your intelligence pipeline takes days. Every hour that gap exists, your exposure grows. Speed is the metric that matters.
NVD, vendor advisories, dark web forums, OSINT feeds. Your analysts juggle it all with no unified view. Priority becomes guesswork. Context gets lost.
The skills gap is real. Your team can't cover every advisory, every CVE, every active campaign. Without a daily brief that cuts the signal for you, something always slips through.
Not linked to another page. Not summarised. Included.
Sigma Detection Rules
Deploy-ready YAML matched to the threat — convert to Splunk, Sentinel, or Elastic with sigma-cli.
WAF Rules — 4 Platforms
ModSecurity, Cloudflare, AWS WAF, and Azure Front Door rules targeting the specific exploit pattern.
IOC Tables
Behavioral, network, and host indicators — copy directly into your SIEM or threat intel platform.
Remediation Steps
Verb-first, prioritized, time-bound. Patch step 1 links directly to the vendor advisory.
Decryption Digest is not a news aggregator. It's a practitioner's action guide, delivered daily, focused on the single most critical threat, and built to give your team a clear mission the moment they start their day.
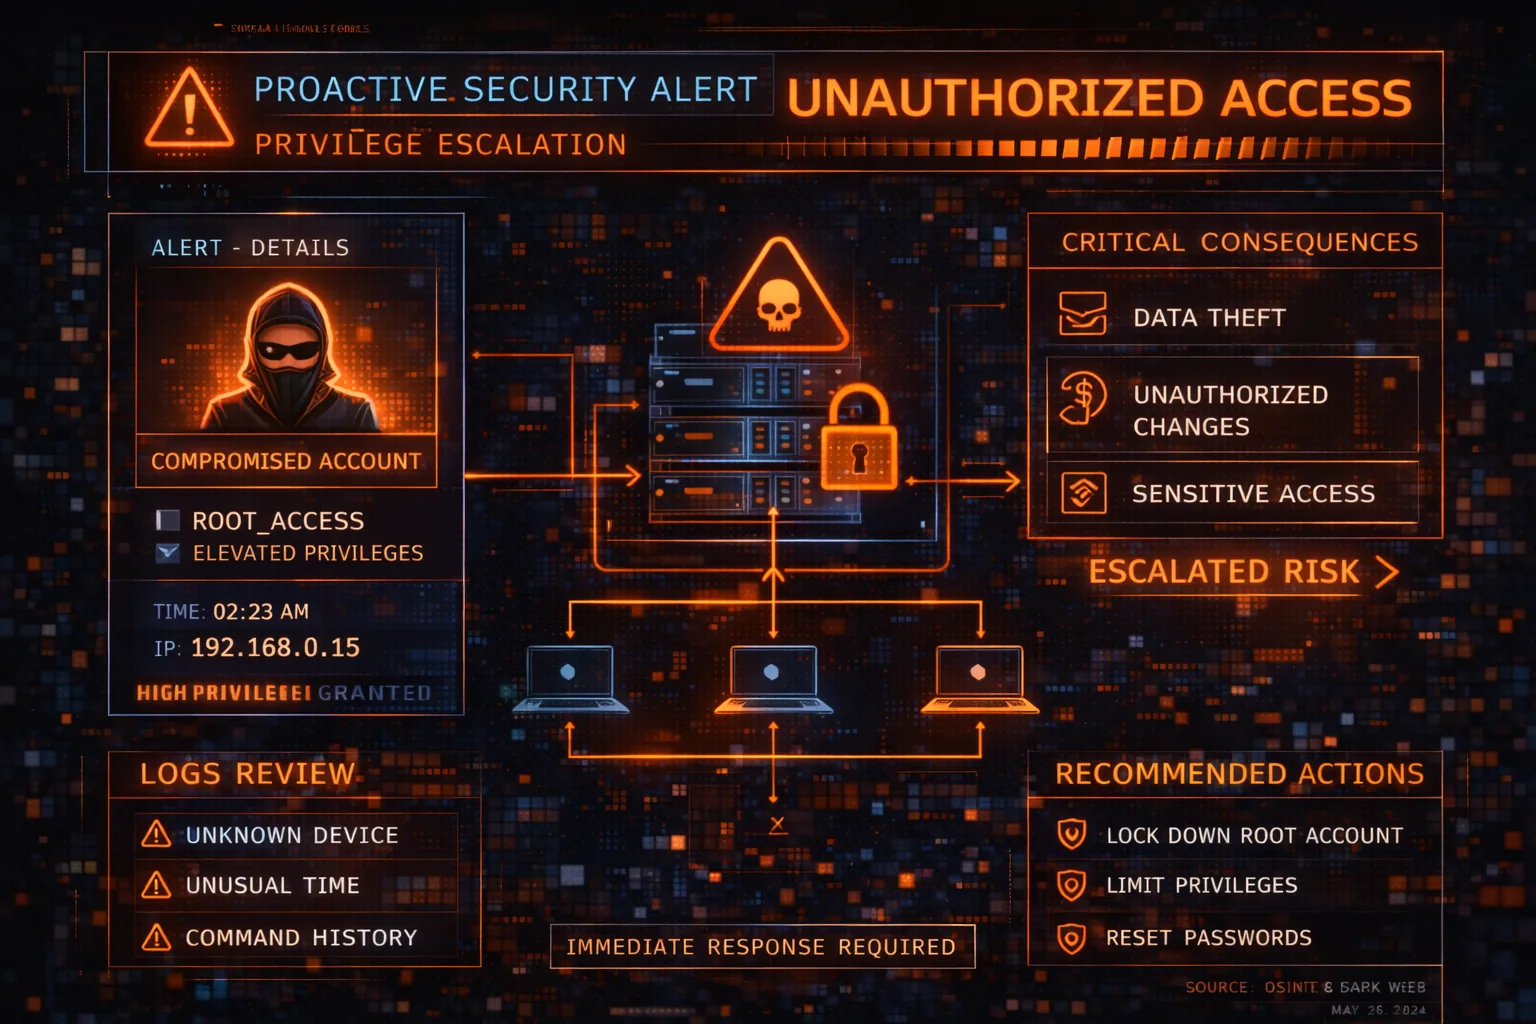
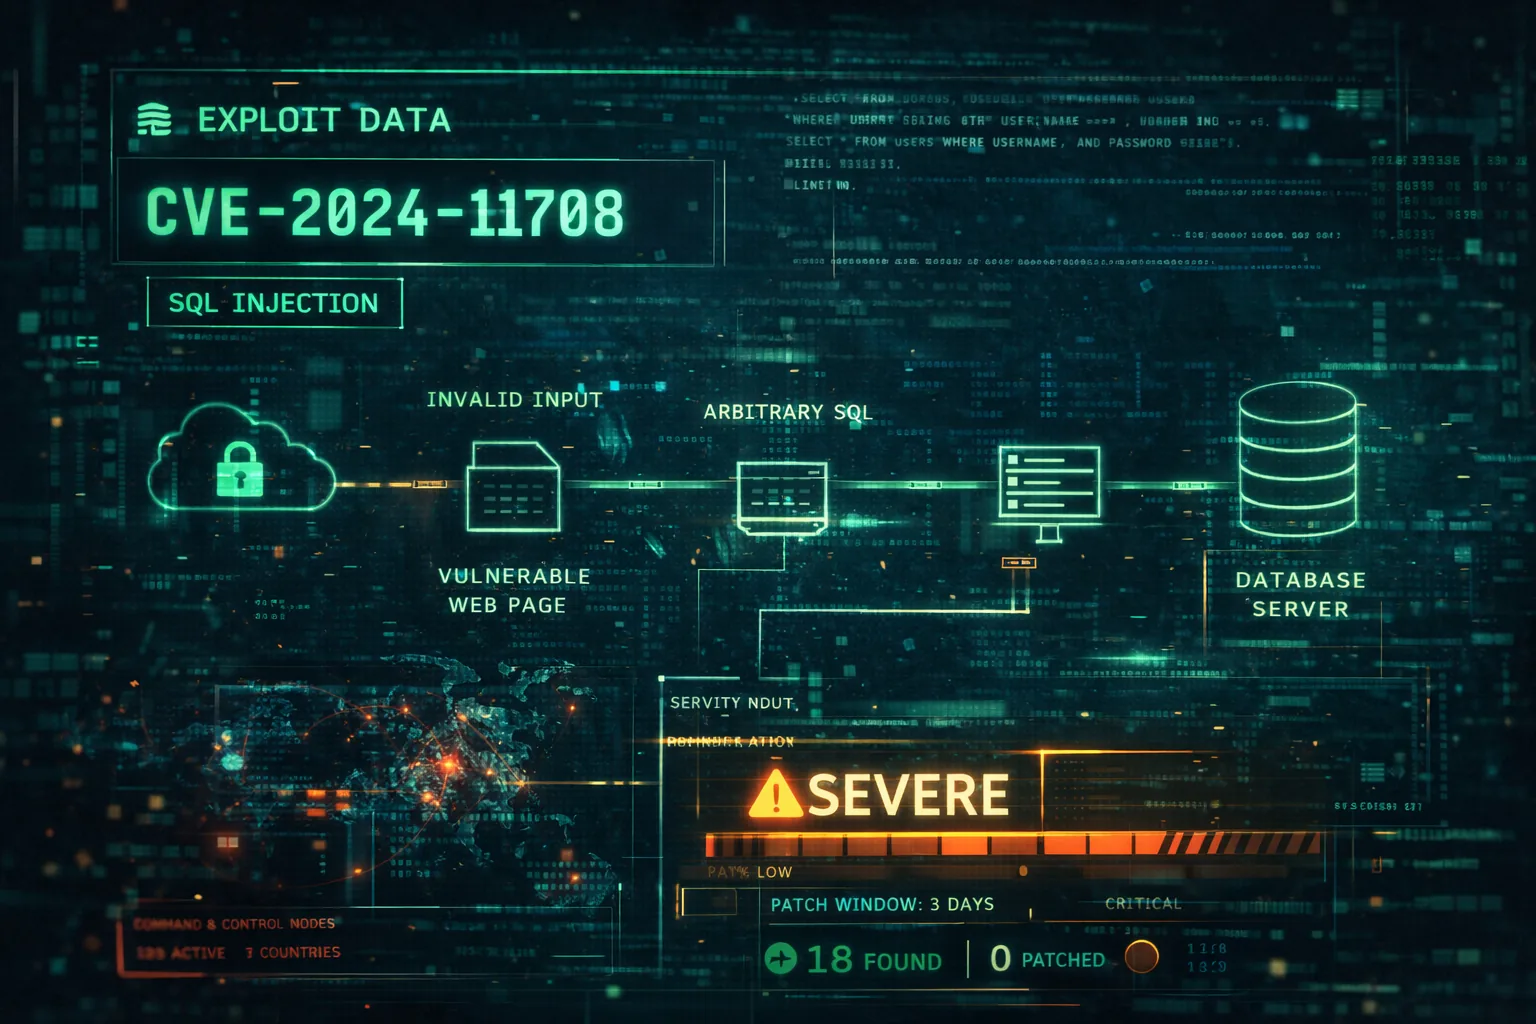
Sample Analysis: CVE Exploit Path Mapping
Every briefing is reviewed for accuracy and real-world impact. No AI hallucinations. No vendor marketing. Just verified intelligence you can trust.
Every morning we identify the single most critical, most actionable threat and tell you exactly what to do. Not a theme, not a list — the one thing that demands your attention today.
Critical alerts reach you within hours of disclosure, not days. Our monitoring pipeline covers NVD, advisories, exploit databases, dark web chatter, and live campaign tracking.
CVSS scores miss the point. We factor in active exploitation, threat actor targeting, industry context, and exploit maturity. So you act on what's actually dangerous, not just theoretically risky.
No 40-page PDFs. Each briefing is structured for fast consumption: the key facts, the affected systems, the remediation steps. Read it before your standup.
If it's not actively exploited or doesn't pose imminent risk, it doesn't make the cut. Your inbox only carries what demands your attention today.
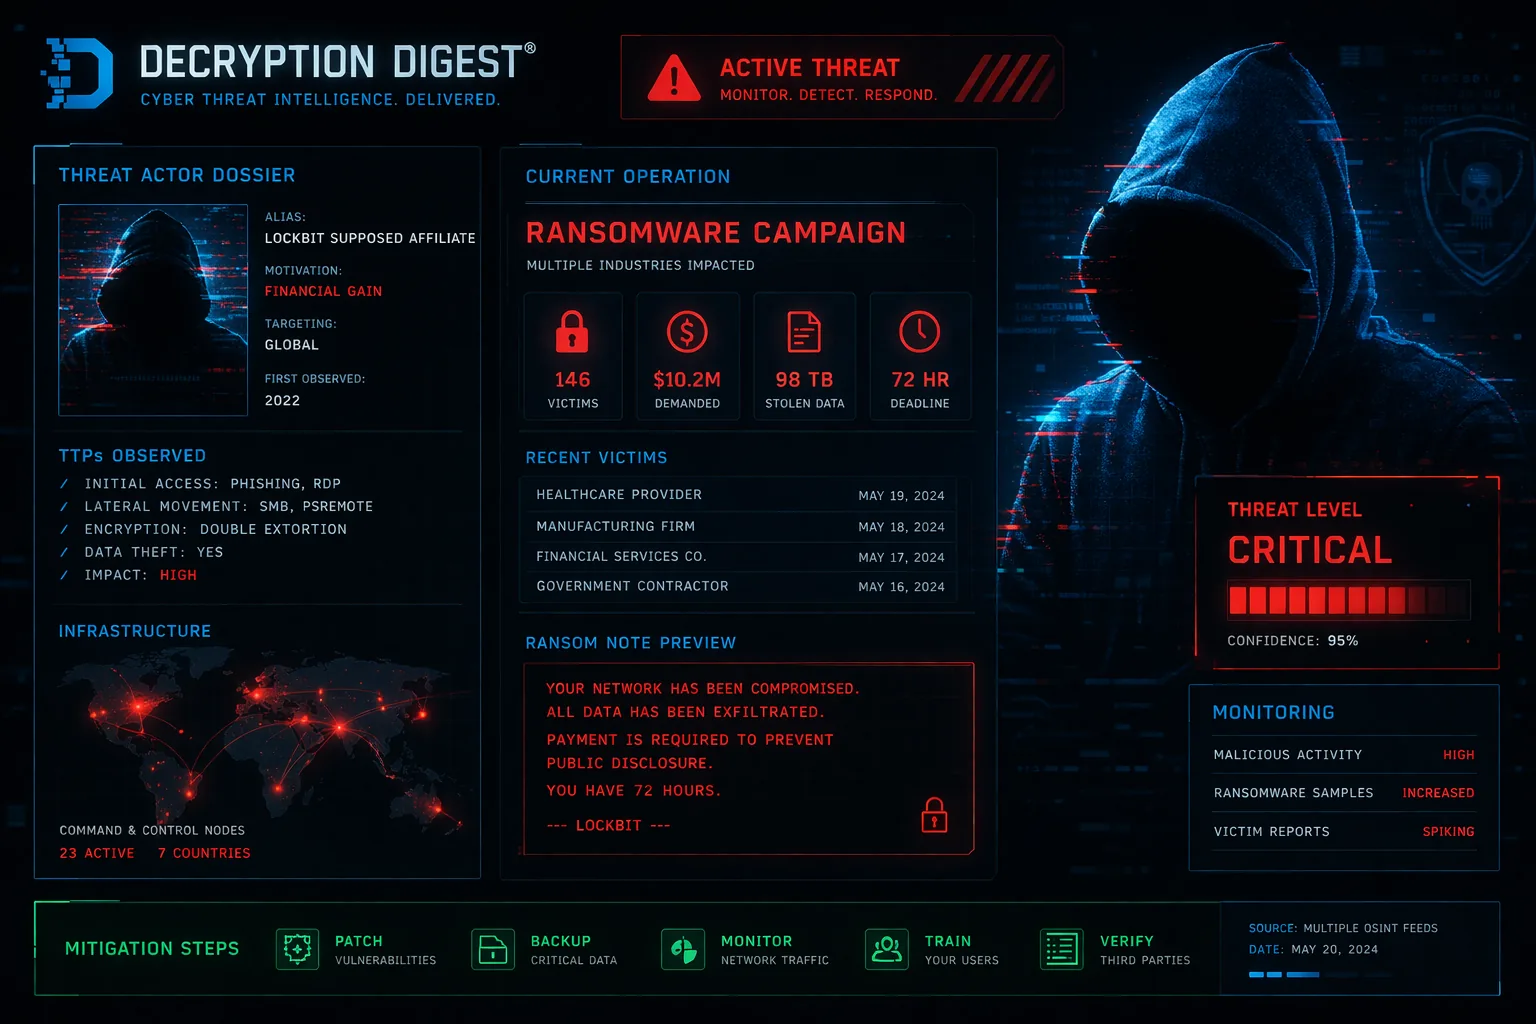
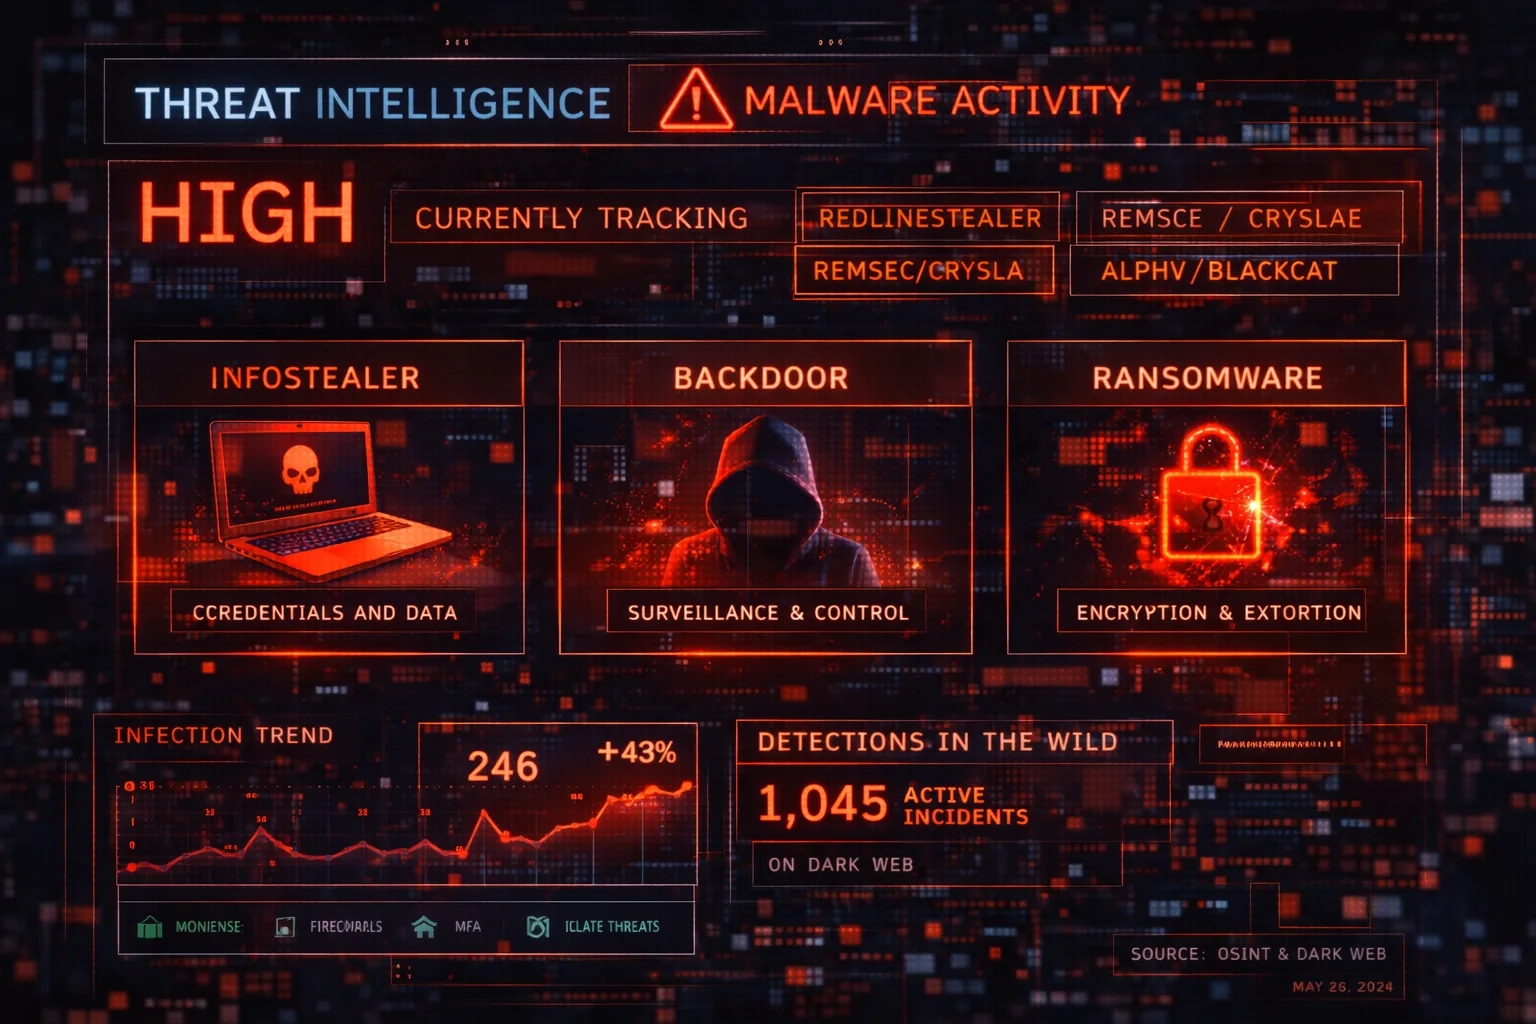
Digest Sample: Ransomware Campaign Analysis
LIVE PREVIEWOur pipeline runs 24/7 across NVD, vendor advisories, exploit databases, threat actor forums, and dark web sources. Nothing critical goes undetected overnight.
Automated triage plus expert analysis. We assess active exploitation, affected industries, and remediation complexity, not just CVSS scores.
We identify the single most critical, most actionable threat from everything we monitored. One post. One clear action. No triage required on your end.
Your team opens the briefing, knows exactly what to act on, and briefs leadership with confidence. Not reactive. Not overwhelmed. Ready.
Trusted by security teams across industries
Decryption Digest cut our mean time to remediate by 40%. We patch what matters first now, instead of chasing every advisory.
I used to spend 2 hours every morning triaging threat feeds. Now I spend 5 minutes reading the digest and my day starts with clarity.
The remediation context is what sets this apart. It's not just 'here's a CVE.' It's 'here's what to do about it and why it matters for your stack.'
Decryption Digest was born from a simple frustration: security teams spending more time parsing intel than acting on it. Founded by veteran threat analysts and incident responders, we built the briefing we always wished we had.
Our team combines deep expertise in vulnerability research, threat hunting, and security operations. We've worked the SOC floors, led red teams, and managed enterprise security programs. We know what matters because we've lived it.
Every day has a purpose. Every briefing drives action. Join 50,000+ SOC analysts, CISOs, and security engineers who start their day with Decryption Digest, the daily security briefing built for practitioners, not executives.
Free. No credit card. Trusted by teams at Fortune 500 companies. Unsubscribe anytime.
Anthropic's AI finds zero-days your scanners miss.
Anthropic's AI finds zero-days your scanners miss.