
Built by defenders,
for defenders.
Decryption Digest is a cybersecurity threat intelligence publication delivering high-signal briefings on zero-days, ransomware campaigns, nation-state operations, and critical CVEs, distilled from hundreds of primary sources into the analysis your team actually needs.
Signal over noise, every time.
The cybersecurity information landscape is saturated. Vendor blogs optimize for SEO. Social media rewards hot takes over verified facts. Alert fatigue has reached crisis levels across the industry.
Decryption Digest exists to cut through it. We monitor hundreds of threat intelligence sources: government advisories, security research labs, dark web forums, ISAC feeds, and original reverse engineering, and synthesize only what matters into structured, analyst-grade briefings.
Our readers are the professionals defending critical infrastructure, Fortune 500 networks, and government systems. They don't have time to parse twenty vendor blogs to understand a single attack campaign. We do that work for them.
How we work
Every Decryption Digest briefing is held to six non-negotiable editorial standards.
Primary sources only
Every briefing cites original vendor advisories, CISA KEV entries, CVE records, and researcher disclosures, not second-hand blog summaries.
Adversary-centric framing
We map threats to MITRE ATT&CK TTPs and attribution where confirmed, giving you context to prioritize response, not just a list of CVE numbers.
Actionable remediation
Every post includes concrete detection queries, patch guidance, and IOC blocks so your team can act immediately, not just understand the threat.
No vendor bias
We are editorially independent. We cover products from all vendors, including when they are the source of the vulnerability.
Timeliness over volume
We publish when a threat is significant and actionable, not on a forced schedule. Your attention is finite; we respect it.
Verified before published
Unconfirmed reports, social media rumors, and single-source claims are never published. We wait for corroboration or official confirmation.
Who reads Decryption Digest
CISOs & Security Directors
Executive-ready threat summaries with business risk context.
SOC Analysts & Threat Hunters
IOC tables, detection logic, and TTP mappings ready to operationalize.
Security Engineers
Technical depth on exploit mechanics, BYOVD chains, and lateral movement.
Incident Responders
Attack chain breakdowns and forensic artifacts to accelerate triage.
Penetration Testers
Real-world TTP analysis straight from active threat campaigns.
GRC & Compliance Teams
Regulatory impact assessments alongside the technical threat analysis.
Sources we monitor
Government & Official
- CISA Known Exploited Vulnerabilities (KEV)
- NIST National Vulnerability Database (NVD)
- US-CERT / ICS-CERT Advisories
- NSA & NCSC Cybersecurity Advisories
- FBI & DOJ Indictments and Alerts
- ENISA Threat Landscape Reports
Security Research
- CrowdStrike, Mandiant, Recorded Future
- Cisco Talos, Palo Alto Unit 42
- Microsoft MSTIC & MSRC
- Google Project Zero & TAG
- Wiz Research, Qualys TRU
- Independent researcher disclosures
Guided by practitioners
Decryption Digest is advised by security leaders across enterprise, military, and academic cybersecurity who help sharpen our editorial focus and coverage priorities.
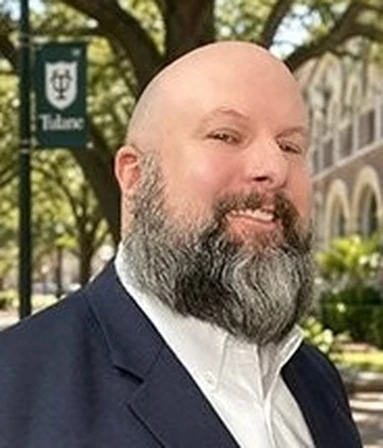
Cybersecurity Executive, Professor, Author, and Military Cyber Leader
Joshua Copeland is a cybersecurity executive with more than 25 years of experience spanning enterprise security, military service, higher education, and public-sector cyber defense. He serves as a cybersecurity director, professor of cybersecurity, and deputy commander of a state cyber reserve force. Joshua is the author of Unpopular Opinion and a frequent keynote speaker, media contributor, and podcast host known for challenging conventional thinking on cybersecurity leadership, governance, and organizational resilience. His work focuses on translating technical capability into timely, coordinated, and mission-driven action.
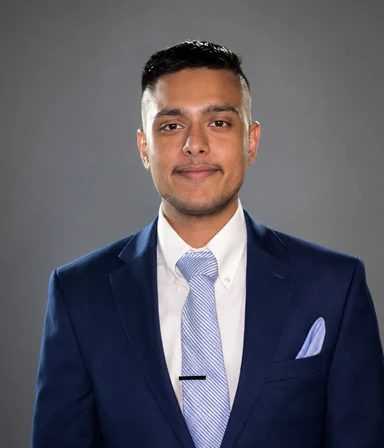
Cybersecurity Threat Intelligence Lead, Insulet Corporation
Janil Patel serves as the Cybersecurity Threat Intelligence Lead at Insulet Corporation, where he built the organization's Cybersecurity Threat Intelligence (CTI) program from the ground up. His work focuses on transforming threat intelligence into actionable insights that strengthen security operations, vulnerability management, and cyber risk management. He currently leads efforts to mature the CTI program by advancing intelligence capabilities, enabling proactive defense strategies, and helping drive informed security decisions across the enterprise. His passion is building intelligence-driven security programs that improve organizational resilience against evolving cyber threats.
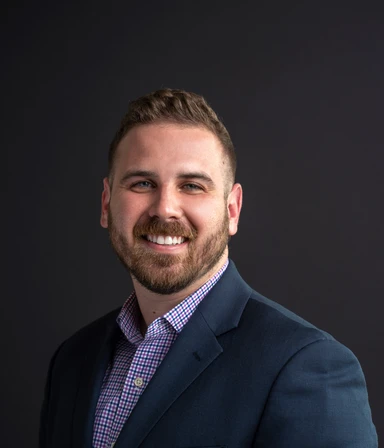
AI Security Leader & Advisor
Jackson brings extensive cybersecurity experience spanning blue team defense strategy, detection and monitoring, and offensive red team operations across organizations of varying sizes and maturity levels. He currently leads and advises on AI security initiatives, with a focus on governance, responsible data handling, risk management, and secure-by-design practices.
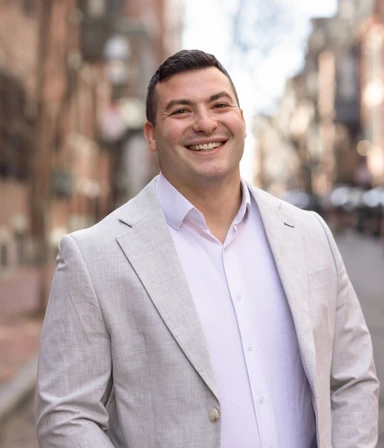
Trusted Advisor, GuidePoint Security
Andrew started his cybersecurity career in 2017 after earning his degree in Business Informatics from Indiana University's Luddy School of Informatics, Computing, and Engineering. He spent four years at IANS Research advising CISOs and security teams across the Fortune 500, learning what it takes to help security leaders make confident, high-stakes decisions. From there, he moved to the vendor side at Silverfort, where he built deep expertise in Identity and Access Management and gained a strong understanding of the broader vendor landscape and ecosystem. Today, Andrew works as a trusted advisor to clients across New England through GuidePoint Security, where his role goes well beyond just recommending tools. He partners closely with security leaders to understand where their real risks live, streamline how their teams operate, and make sure security stays aligned with where the business is headed. Whether he's acting as a technical integrator or a sounding board when a client needs to think something through, Andrew's focus stays on reducing risk and helping organizations move forward with confidence.
Read it every morning, free.
Join 50,000+ SOC analysts, CISOs, and security engineers who start their day with Decryption Digest.
Questions, tips, or sponsorship?
We welcome verified threat tips, research collaboration requests, and sponsorship inquiries from vendors reaching security-focused audiences.